01
SIEM: event aggregation and correlation
Logs from servers, network devices and systems are centralized in the SIEM, and scattered events are correlated so the pattern of an attack stands out from normal activity.
SECURITY OPERATIONS CENTER
The Razban SOC reads the events and logs from your infrastructure around the clock, spots suspicious behavior and responds when an incident starts. It is built on 14 years of operating experience, covers more than 130 organizations and responds in under 15 minutes on average.
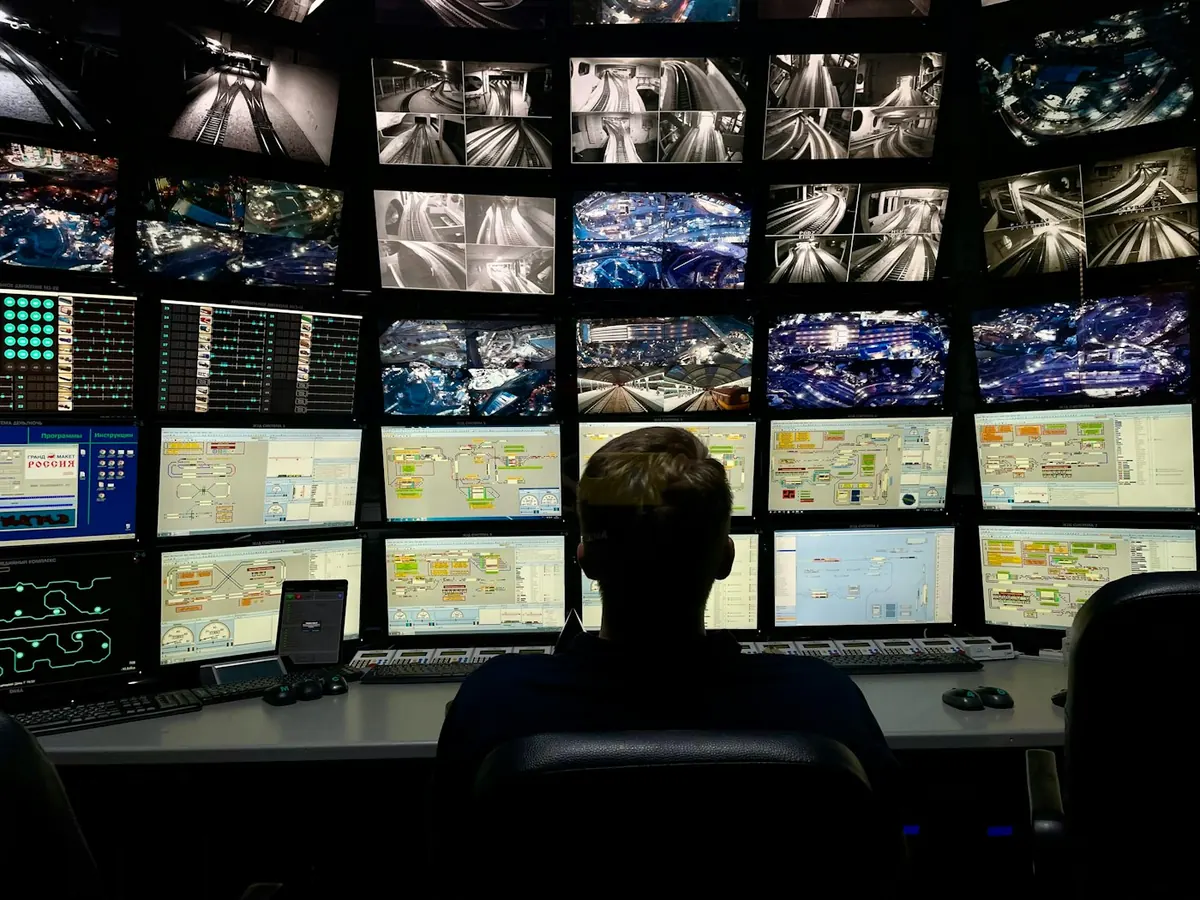
The Razban SOC rests on three pillars, SIEM, MDR and Threat hunting, and watches events from your endpoints, network and cloud services in a single view.
Logs from servers, network devices and systems are centralized in the SIEM, and scattered events are correlated so the pattern of an attack stands out from normal activity.
Razban analysts detect threats and act to contain them as a managed service, and the outcome of every action is coordinated with you.
Beyond reviewing alerts, analysts actively search the collected data for signs of an intrusion that has not yet triggered an alert.
Events from workstations and servers, network devices and your cloud services are reviewed together, so an attack can be traced as it moves between them.
Indicators of known threats and new attack patterns feed into the detection rules, and those rules are updated continuously.
Repetitive responses to known incidents run automatically, which keeps response times short and frees analysts to focus on complex incidents.
Every security alert at the Razban SOC follows this path, from the first sign of trouble to full service recovery.
Events from your infrastructure are received continuously, at every hour of the day.
Detection rules and threat hunting separate suspicious behavior from normal activity, and an alert is raised.
An analyst reviews the alert to tell a real incident from a false positive and to assess its severity.
For a real incident, containment steps are taken or reported to you according to the agreed escalation path, so the incident does not spread.
The people named in the escalation path are notified, and next steps are coordinated with your IT team.
Service recovery is followed through, corrective recommendations are made to prevent a repeat, and the incident is recorded in the monthly report.
We list which servers, devices and applications will send logs.
The logs are connected and detection rules are tuned.
We agree who is called, and when, for each type of incident.
Monitoring starts, with a report every month.
Monitoring runs at every hour of the day, and the Razban SOC responds in under 15 minutes on average.
Monitoring tells you whether servers, networks and services are up and performing. A security operations center analyzes security events and responds to security incidents. Many organizations run both.
No. The SOC detects, analyzes and contains incidents, and coordinates the necessary actions with your IT team along the escalation path. Decisions about your systems stay with that team.
The monthly report shows the security posture of your infrastructure with measurable indicators and includes corrective recommendations to reduce the risks identified.
A list of the servers, network devices and systems to be monitored, and where their logs are kept. We review the list in the first meeting and propose how to connect each source to the SOC.
Yes. The paid version of Razban Shield connects a website or server to Razban Cloud and puts it under SOC monitoring.
Tell us about your servers, network devices and applications and where their logs are kept, and we will propose how to connect them to the SOC.